By Ronnie Mbuqe
The server can commit a change and lose the connection before the client receives confirmation. The browser sees uncertainty while the database contains a result.
A blind retry may repeat the operation. Systems need a way to identify the original request or safely check its outcome.
The padlock protects the connection; it does not certify an honest shop
A convincing shop can use HTTPS and still fail to deliver what it promises. Connection security and the merchant's intentions are different questions. A browser cannot turn the second into a guarantee merely by encrypting the first.
We will separate the address, request, response and business outcome. You should finish able to say what a status code establishes and what it leaves for the application or person to check.
Does HTTPS prove that a website's claims are true?
HTTPS helps protect data in transit and authenticate the contacted host through certificates.
Trace the explanation
A misleading business can still operate an HTTPS site. Check the destination and the claim as well as the connection security.
Source and further reading: MDN Web Docs
Read the response in layers
A browser requests a resource from a particular domain. The response includes a status, headers and usually a body. A 200 status can indicate a successful retrieval even if the content contains an incorrect claim.
Likewise, a business API might document a response body that reports a declined action. Its caller must interpret that contract rather than treating any received body as success. Different services use different conventions; the documentation and observed response need to agree.
Check the actual domain independently when a request involves payment or credentials. A fraudulent domain can have its own valid certificate. HTTPS remains essential transport protection, but evaluating the business requires additional evidence.
A resource retrieval returns status 200. Does that alone establish that every factual statement on the page is true? Type yes or no.
This checks a prediction about the worked example. It does not run server code, contact an API or change a booking.
No. Protocol success is not a fact check of the response content or a guarantee of the merchant's conduct.Read the explanation without the checker
No. Protocol success is not a fact check of the response content or a guarantee of the merchant's conduct.
Compare a page that loaded correctly with a checkout action that was accepted. Explain why these are different claims even when both use HTTP.
A padlock cannot tell you a shop is honest
HTTPS protects the connection to the named site using encryption and authentication mechanisms. A fraudulent shop can also obtain a certificate for its own domain. A protected connection and a trustworthy business are different claims.
Check the actual domain and the transaction context. A look-alike address can be encrypted just as a legitimate address can. Transport security prevents important kinds of interference, but it does not inspect the merchant's intentions or guarantee delivery of goods.
Practical examples: HTTP
Opening
Opening one URL starts an HTTP request for the HTML document. After reading it, the browser may request styles, scripts, fonts and data separately. The completed page is assembled from responses that can arrive from different servers and caches.
Submitting
Submitting a form sends values with a method such as POST. The server validates them and may return errors, redirect after success or create a record. HTTPS encrypts the journey, but validation and authorisation still decide whether the requested action is allowed.
Calling
A browser calls an API using the same protocol but often expects JSON instead of a complete page. Status codes distinguish success, missing resources, invalid input, forbidden access and server failure so the client can show an honest state.
Loading
Images and other static files use HTTP caching rules so the browser can reuse unchanged content. Correct cache headers reduce loading time and server work, while versioned URLs let a site publish a new file without leaving users stuck on an old copy.
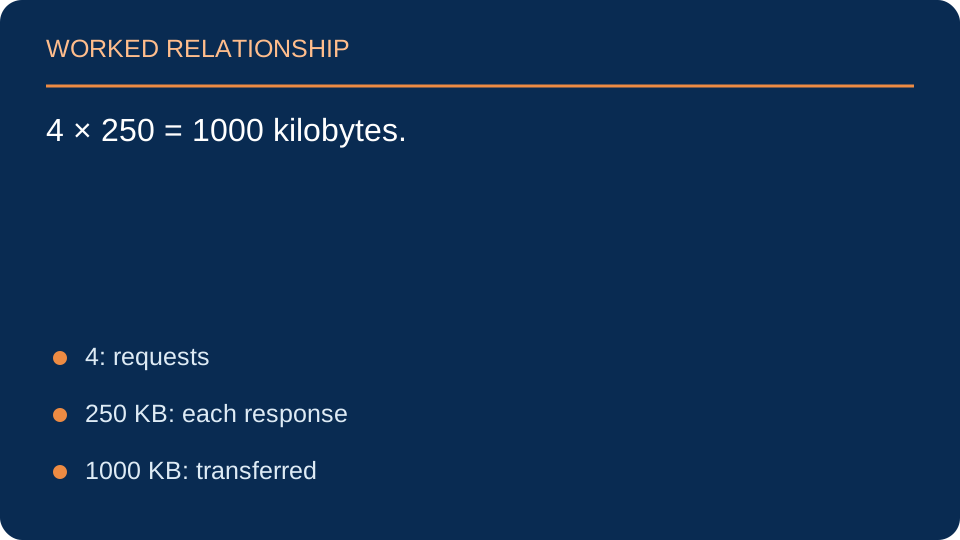
A page makes 4 requests that each transfer 250 kilobytes in a simplified example. How many kilobytes are transferred?
Trace the explanation
4 × 250 = 1000 kilobytes. This ignores protocol overhead and compression. Counting requests alone cannot establish data cost because response sizes differ.
Source and further reading: MDN Web Docs
Why does HTTPS not guarantee that a website tells the truth?
HTTPS protects the connection to the identified endpoint. It does not establish that every statement on the page is accurate or that a seller is honest.
A deceptive site can also use encryption. Check the actual domain, the source of a claim and the relevant business details in addition to the connection indicator.
Why a page can look partly loaded and still be waiting
The first HTML response may refer to stylesheets, scripts, fonts and images that need further requests. Some resources can be cached, some can fail, and some scripts start additional data calls. The visible page is assembled from a network of dependencies rather than one indivisible download.
The latency explorer adds an illustrative network delay to server work. Real requests can overlap and reuse connections, so the model is not a benchmark. Its purpose is to show why reducing one server calculation does not eliminate time spent waiting on communication or missing resources.
Does HTTP 200 prove that the page's information is correct?
No. It indicates the request was handled successfully according to HTTP semantics. The representation can still contain stale data, a misleading claim or a business-level failure if the service contract permits that.
Questions about HTTP Explained Simply
What is HTTPS?
HTTPS is the secure version of HTTP. It helps protect information as it travels.
What is a 404 error?
It means the requested page or resource was not found. The server received your request and understood it, but nothing exists at that address, similar to a courier reaching the right street but finding no house at that number.
What is the difference between GET and POST?
GET is generally used to retrieve a resource, while POST commonly sends data that creates or triggers work. The exact meaning is defined by the API, but those conventions make systems easier to understand.
What is a status code?
It is a three-digit result included in an HTTP response. Codes in the 200 range indicate success, 300 range redirection, 400 range client/request problems and 500 range server failures.
Why are headers useful?
Headers carry information about the message, such as content type, caching rules, authentication, accepted formats and security instructions.
A secure-looking link has a misspelled bank domain. Which risk does the padlock fail to eliminate?
One reasoned response
An encrypted connection to the wrong organisation is still the wrong destination. Verify the actual domain and use a trusted route rather than treating the lock symbol as a business endorsement.
Source and further reading: MDN Web Docs
Example: understand a request and response
HTTP is the protocol browsers and servers use to exchange web requests and responses. A simplified request for a page might look like this:
GET /learning/ HTTP/1.1
Host: example.test
Accept: text/html
The server responds with a status code, headers and possibly a body containing HTML. A 200 status usually means the request succeeded; a 404 means the requested resource was not found; and a 500 indicates a server-side failure. These codes are clues, not complete diagnoses. Redirects, caching, authentication and content negotiation can change the path. HTTPS protects HTTP traffic in transit, but it does not guarantee that a website's claims are honest or that its application has no security flaws.
Sources
Sources and further reading
A closer lookThe same screen can hide different failures
A browser loads a booking page, then a separate availability request fails. The page itself may have loaded successfully while the later request received an error.
Work through the distinction
Use the network panel to inspect the failing request's URL, status and response. A status code belongs to a particular exchange. Successful page delivery does not establish that every script, image and API call also succeeded.
What should you inspect first?
Choose an answer to see feedback. You can try again.
Show the answer and explanation
The specific failed network request. Use the network panel to inspect the failing request's URL, status and response. A status code belongs to a particular exchange. Successful page delivery does not establish that every script, image and API call also succeeded.